AI Agents Hacked 100+ Company Websites: How One Hacker Targeted 1,200 Sites
AI Agents Hacked 100+ Company Websites
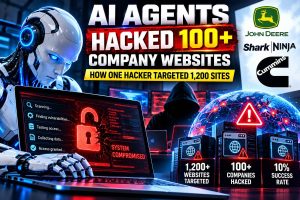
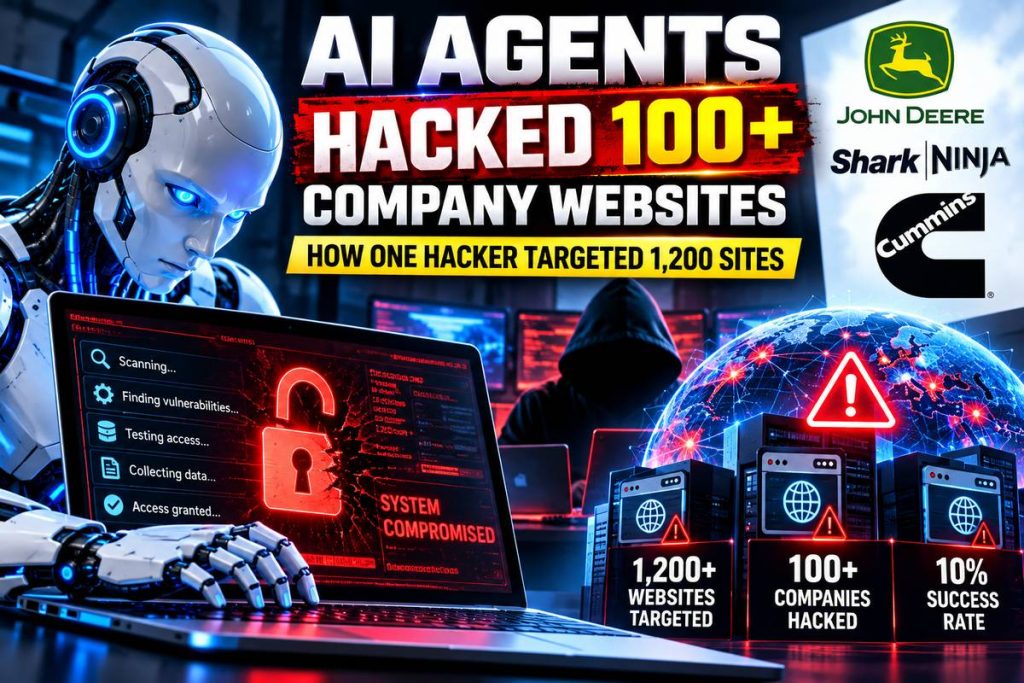
A single hacker used autonomous AI agents to target more than 1,200 websites and gain access to sites associated with more than 100 companies, according to cybersecurity researchers and reporting published in October 2026.
Companies identified in reporting included:
- Deere & Company;
- SharkNinja; and
- Cummins.
The campaign is one of the clearest real-world examples yet of how AI agents can dramatically scale cyberattacks.
Instead of manually investigating every website, the operator could give an AI system a target and objective, then allow autonomous agents to spend hours researching the site, testing possible weaknesses and adapting their approach.
Security firm NorForge says it discovered more than 20 publicly exposed control panels running Cairn, an open-source AI problem-solving framework being used by several actors for malicious cyber operations.
The largest cluster contained more than:
1,100 attack projects.
NorForge estimated an average success rate of roughly:
10%.
For successful projects in the most active cluster, the average time from start to the attacker’s defined goal was slightly under:
23 hours.
And the estimated AI-model cost was remarkably low.
NorForge estimated that an average task could cost around:
$5 in AI usage
although the company stressed that the estimate has considerable uncertainty.
Reuters separately estimated that successful compromises could work out to roughly:
$50 per successful breach
based on the observed campaign.
The important story is not simply that AI was involved.
It is that one human operator could delegate large amounts of repetitive cybersecurity work to autonomous agents simultaneously.
That changes the economics of online attacks.
Here is what happened, how AI agents were used, and what website owners should do about the growing risk of AI-powered cyberattacks.
What Happened in the AI Website Hacking Campaign?
Cybersecurity researcher Snorre Fagerland of NorForge discovered publicly accessible control panels running a platform called:
Cairn.
Cairn is a state-based AI problem-solving engine.
An operator provides:
a starting point
and:
a goal.
AI workers then attempt to progress toward that goal by gathering information, making decisions and deciding what to try next.
NorForge found that some operators were using this type of system for legitimate security work.
Others appeared to be using it for:
real criminal cyberattacks.
The company ultimately identified more than:
20 exposed Cairn panels
that it considered likely connected with malicious activity.
Those exposed systems gave researchers an unusual opportunity to observe autonomous AI-driven attacks as they happened.
How Many Websites Did the AI Agents Target?
Reuters reported that the most active hacker targeted more than:
1,200 websites.
NorForge’s largest observed activity cluster contained more than:
1,100 individual attack projects
across:
14 Cairn dashboards.
The targets were concentrated largely in:
- the United States;
- Japan;
- Australia;
- Canada; and
- other commercial markets.
The campaign focused heavily on:
e-commerce and payment-related websites.
That makes the incident particularly relevant to:
- online stores;
- WordPress websites;
- WooCommerce businesses;
- Magento stores;
- payment platforms;
- retailers; and
- small businesses operating multiple websites.
How Many Companies Were Breached?
Reuters identified websites associated with more than:
100 companies
that appeared to have been successfully compromised.
Reported companies included:
Deere
SharkNinja
and:
Cummins.
However, the impact differed between organizations.
Deere told Reuters it had taken remedial action and said there was no indication sensitive information had been accessed.
SharkNinja confirmed a breach involving a standalone product-support website and said the issue had been contained.
Cummins investigated activity involving a website operated by a third-party vendor.
Therefore, it would be inaccurate to assume every company experienced the same level of compromise or data loss.
The full extent of data theft, if any, remains unclear.
Was This Really Autonomous AI Hacking?
Yes—but with an important qualification.
This was not an AI system spontaneously deciding to attack companies on its own.
A human operator:
- selected targets;
- defined goals;
- configured the infrastructure; and
- initiated the campaigns.
The AI agents then performed large portions of the work autonomously.
That makes the best description:
human-directed, AI-executed cyberattacks.
This distinction matters.
AI did not independently decide to become a cybercriminal.
A human criminal used increasingly capable AI agents as force multipliers.
What Is Cairn?
Cairn is a general-purpose AI problem-solving framework.
NorForge explains that a Cairn project begins with:
an origin
and:
a goal.
AI agents then work through multiple stages.
As they operate, they record:
- information discovered;
- possible next actions;
- observations;
- results.
The system can continue working toward the objective over an extended period rather than waiting for a human to manually provide every next instruction.
That is what makes the technology:
agentic.
The system is capable of pursuing a goal through a sequence of decisions and actions.
For a broader explanation, read our guide to What Is Agentic AI?.
Why AI Agents Change Cybersecurity
Traditional hacking often requires significant human time.
An attacker may have to:
- research a target;
- identify technologies being used;
- search for potential vulnerabilities;
- test possible weaknesses;
- analyze errors;
- change the approach;
- repeat the process.
That becomes expensive when repeated across hundreds or thousands of websites.
AI agents change the equation.
One person can potentially launch many autonomous tasks simultaneously.
Each agent can spend hours working through a target while the human operator focuses somewhere else.
This creates a new form of scale.
The danger is not necessarily that AI suddenly becomes a better cybersecurity expert than every human.
The danger is that:
one attacker can automate work that previously required a much larger team.
How Much Did the AI Attacks Cost?
NorForge estimated the average AI-model cost for a task at roughly:
$5.
However, the company cautioned that the estimate is uncertain.
Some complicated projects could cost considerably more.
Longer-running tasks containing hundreds or thousands of AI interactions could exceed:
$100.
Reuters estimated the broader campaign cost at roughly:
$5,000 in AI usage
and around:
$50 per successful compromise.
These numbers should be treated as estimates rather than audited financial figures.
But even with uncertainty, the larger conclusion is difficult to ignore:
AI can make large-scale cyber operations much cheaper.
How Long Did the AI Agents Work on Each Website?
For successful projects in NorForge’s largest observed cluster, the average time between the project beginning and reaching its goal was:
slightly under 23 hours.
Some tasks lasted much longer.
One observed project reportedly continued for more than:
five days.
This is another reason AI agents change the security landscape.
Humans need sleep.
Software agents do not.
An automated system can continue researching, testing and adapting:
24 hours a day.
What Was the Success Rate?
NorForge estimated that the AI hacking frameworks observed had an average success rate of approximately:
10%.
That does not mean every ten websites on the internet can be hacked by AI.
The target selection was not random.
The attackers deliberately chose websites they considered promising.
The definition of “success” also varied between projects.
NorForge itself describes the 10% figure as a reasonable estimate rather than a precise measurement.
Still, even a relatively low success rate becomes significant at scale.
If one operator can cheaply test:
1,000 websites
a 10% success rate could potentially produce:
100 successful compromises.
That is why automation matters.
Why Were the Hackers’ Own AI Systems Exposed?
Ironically, the attackers made serious security mistakes themselves.
NorForge discovered many of the Cairn control panels because they were:
publicly accessible on the internet without appropriate protection.
These panels exposed substantial information.
Researchers could see:
- attack projects;
- target information;
- AI-agent activity;
- discovered weaknesses;
- credentials;
- API keys;
- project status.
NorForge says it found hundreds of secrets in the exposed data.
Some were still valid.
In other words:
the hackers were using AI to find other people’s security mistakes while making major security mistakes of their own.
Why This Matters to Small Website Owners
The companies named in news coverage are large.
But the lesson may be even more important for smaller websites.
Attack automation makes it economically practical to investigate targets that a human attacker might previously have ignored.
A small e-commerce site may not seem valuable enough for an experienced hacker to manually spend hours studying.
But an autonomous agent does not have the same economics.
If investigating a site costs only a few dollars in AI usage, attackers can potentially examine:
- small online stores;
- forgotten subdomains;
- old landing pages;
- outdated staging environments;
- vendor-managed websites;
- microsites;
- abandoned applications.
That means being “too small to hack” becomes an increasingly dangerous assumption.
Forgotten Websites May Become a Bigger Risk
One particularly important lesson from the reported victims is that attackers may not always target a company’s primary homepage.
Organizations often maintain many different web properties.
Examples include:
- support websites;
- product microsites;
- regional websites;
- old campaign pages;
- vendor-hosted portals;
- staging environments;
- discontinued product sites.
These sites may receive less security attention than the main corporate website.
AI agents are well suited to finding overlooked infrastructure because they can continuously search and evaluate large numbers of possible targets.
That makes asset inventory increasingly important.
A company cannot secure websites it has forgotten it owns.
What Does This Mean for WordPress Website Owners?
WordPress powers a large portion of the web and is therefore naturally attractive to automated scanning.
The Cairn campaign does not mean WordPress itself was specifically responsible for the attacks.
But WordPress owners should pay attention to the broader pattern.
Attackers increasingly automate searches for:
- outdated software;
- exposed administrative interfaces;
- weak authentication;
- forgotten sites;
- old plugins;
- outdated themes;
- misconfigured servers.
The recent PHP2Shell incident provides another example of why underlying website infrastructure needs attention.
Read our guide to PHP2Shell and the critical PHP vulnerabilities affecting WordPress websites.
What Website Owners Should Do Now
The response to AI-powered hacking is not some special “anti-AI” security product.
The most effective defenses remain strong cybersecurity fundamentals.
But they need to be applied more consistently and more quickly.
1. Know Every Website You Own
Create an inventory of:
- domains;
- subdomains;
- WordPress sites;
- e-commerce stores;
- staging environments;
- support portals;
- old campaign sites;
- vendor-hosted applications.
If a website is no longer needed:
shut it down.
An abandoned application still connected to your company can become an attack path.
2. Patch Software Quickly
Keep current:
- CMS software;
- WordPress core;
- plugins;
- themes;
- PHP;
- e-commerce platforms;
- server packages.
AI agents can accelerate the process of identifying systems that have not been patched.
That reduces the comfortable window businesses once had between:
vulnerability disclosure
and:
real-world attacks.
3. Remove Plugins and Applications You Don’t Use
Disabling unused software is better than leaving it active.
Deleting unnecessary software is usually better still.
Every plugin, theme, web application and administrative interface adds potential attack surface.
4. Use Multi-Factor Authentication
Require MFA for:
- website administrators;
- hosting accounts;
- domain registrars;
- cloud platforms;
- email accounts;
- CDN accounts;
- developer tools.
A stolen password should not automatically provide full access.
5. Protect Hosting Accounts
Website security is not only about WordPress.
An attacker who compromises:
your hosting account
may be able to bypass many application-level protections.
Use:
- unique passwords;
- MFA;
- limited administrator access;
- login alerts;
- regular account reviews.
6. Use a Web Application Firewall
A WAF can help detect and block suspicious traffic before it reaches the application.
Cloud-based security services can also help identify automated probing.
A WAF does not replace:
patching.
Think of it as another layer.
The strongest approach is:
updated software + WAF + secure accounts + monitoring + backups.
7. Monitor Logs
AI-driven attacks may involve long periods of automated investigation.
Monitoring can help identify unusual:
- requests;
- authentication failures;
- new administrator accounts;
- file changes;
- unexpected traffic;
- server processes.
Businesses that never review logs can miss early warning signs.
8. Secure Third-Party Vendors
The Cummins-related incident highlights another important issue:
your cybersecurity exposure includes vendors.
Ask third-party website providers:
- Who patches the website?
- Who monitors security?
- Who controls administrator accounts?
- Is MFA required?
- How are backups handled?
- What happens if a breach occurs?
A vendor-managed website still carries your company name.
9. Maintain Offline or Isolated Backups
Backups should not exist only inside the same hosting environment.
Maintain recent copies of:
- files;
- databases;
- configuration;
- critical business information.
Test whether the backup can actually be restored.
A backup you have never tested is only a theory.
10. Remove Publicly Exposed AI Agent Dashboards
This incident also carries a warning for businesses using AI agents legitimately.
Do not deploy agent-management interfaces directly on the public internet without appropriate:
- authentication;
- network restrictions;
- encryption;
- access controls;
- monitoring.
Agent systems may contain extremely sensitive information, including:
- credentials;
- API keys;
- internal data;
- customer information;
- instructions;
- connected-tool access.
Giving an AI agent powerful tools while leaving its management interface unsecured creates an obvious security risk.
AI Agents Are Powerful Because They Can Use Tools
The same capability that makes agents valuable to businesses also creates security risks.
An AI agent can potentially:
- use browsers;
- interact with APIs;
- analyze data;
- run code;
- search systems;
- make decisions;
- repeat actions.
These capabilities are useful for legitimate automation.
Our guide to AI Agents for Small Business explains practical business applications.
But more capability means permissions need to be managed carefully.
The rule should be:
give an AI agent the minimum access it needs.
AI Cybersecurity Is Now an Arms Race
Artificial intelligence is helping both sides.
Defenders can use AI to:
- analyze logs;
- identify vulnerabilities;
- prioritize patches;
- investigate suspicious activity;
- examine code;
- detect anomalies.
Attackers can use AI to:
- automate reconnaissance;
- process large amounts of information;
- scale repetitive work;
- adapt attack strategies;
- investigate many targets simultaneously.
The result is an emerging cybersecurity arms race.
The important variable may increasingly become:
speed.
Who finds the vulnerability first?
Who patches first?
Who notices the attack first?
Who can respond fastest?
Does This Mean AI Agents Are Dangerous?
AI agents are tools.
Their safety depends heavily on:
- who operates them;
- what permissions they have;
- what goals they are given;
- what safeguards exist.
Cairn was not inherently created to become a criminal hacking system.
The incident demonstrates how flexible technology can be repurposed by malicious actors.
The same is true of many cybersecurity tools.
A vulnerability scanner can help a company secure its network.
The same scanner can help a criminal find weak systems.
The technology itself does not eliminate human responsibility.
Could One Hacker Now Replace an Entire Hacking Team?
Not completely.
Advanced cyberattacks still require expertise.
AI agents make mistakes.
They can:
- misunderstand systems;
- waste time;
- follow false leads;
- produce incorrect conclusions.
Many projects observed by NorForge did not successfully reach their goal.
But the important change is:
one skilled operator can supervise much more work.
That is a meaningful shift.
The attacker no longer has to personally perform every repetitive action.
Are AI Agents Better Hackers Than Humans?
That is not what the Cairn campaign proves.
The more accurate conclusion is:
AI agents can dramatically increase human scale.
A skilled hacker might deeply investigate one target.
An AI-enabled operator can potentially investigate hundreds.
Human expertise remains important for:
- choosing targets;
- designing objectives;
- infrastructure;
- interpreting results;
- monetization;
- advanced decisions.
AI reduces the amount of repetitive manual work required.
How Does This Connect to Agentic AI?
The campaign is a real-world example of agentic AI.
Agentic AI moves beyond:
prompt → answer
toward:
goal → plan → action → observation → adaptation → result.
That same loop can be used for legitimate tasks such as:
- research;
- customer service;
- data analysis;
- software development.
But it can also be misused.
Our complete Agentic AI guide explains how these systems work.
Is This Connected to AI Systems Acting on Their Own?
There is an important difference between:
autonomy
and:
independent intent.
The agents in this campaign were autonomous in how they pursued assigned tasks.
But they did not independently decide which companies to attack for criminal purposes.
Humans provided the goals.
That distinction also matters in broader AI-safety discussions.
Elite Era Trends has previously examined incidents involving AI agents behaving unexpectedly in our guides:
and:
Those stories concern different circumstances, but together they illustrate why increasingly autonomous AI systems require:
- monitoring;
- limits;
- permissions;
- containment;
- human accountability.
Frequently Asked Questions
Did AI agents really hack more than 100 companies?
Reuters reported that AI agents used by a hacker gained access to websites associated with more than 100 companies after targeting more than 1,200 sites. NorForge’s investigation provided much of the underlying technical evidence.
Which companies were affected?
Reuters identified companies including Deere, SharkNinja and Cummins. The severity and nature of the incidents differed, and full data-loss details remain unclear.
How many websites were targeted?
More than 1,200 websites were reportedly targeted during the broader campaign.
What AI tool did the hacker use?
The attackers used deployments of an open-source AI problem-solving platform called Cairn.
Was Cairn designed for hacking?
Cairn is a general-purpose state-based problem-solving system that can coordinate AI workers toward goals. NorForge observed criminals using deployments of the framework for cyberattacks.
How much did the AI hacking campaign cost?
NorForge estimated around $5 of AI usage for an average task, though it warned that the figure has significant uncertainty. Reuters estimated successful compromises at roughly $50 each and the broader campaign at about $5,000 in AI costs.
How successful were the AI agents?
NorForge estimated an average success rate of around 10% for the attack frameworks it observed. The company describes this as an estimate rather than a precise measurement.
How long did successful attacks take?
Successful projects in the main observed cluster reached their defined goal in slightly under 23 hours on average.
Did AI choose the companies to attack?
No. Human operators selected targets and goals. AI agents performed much of the subsequent work autonomously.
Were WordPress websites targeted?
The campaign broadly targeted e-commerce and payment infrastructure. The larger risk applies to many web technologies, including WordPress environments when software, infrastructure or accounts are insecure.
Can AI agents hack any website?
No. Whether a website can be compromised depends on actual vulnerabilities, configuration, software versions, credentials, permissions and security controls.
How can I protect my website from AI hacking?
Keep software patched, inventory all websites, remove unused systems, use MFA, protect hosting accounts, use a WAF, monitor logs, maintain backups and secure third-party vendor access.
Is AI making cybercrime cheaper?
The Cairn campaign suggests AI can significantly reduce the cost of repetitive cybersecurity work and let a single operator investigate many more targets.
The campaign uncovered by NorForge marks an important moment in cybersecurity.
A single hacker reportedly used AI agents to:
target more than 1,200 websites
and gain access to sites associated with:
more than 100 companies.
The AI systems worked for hours at a time with relatively little human intervention.
NorForge estimated:
about a 10% success rate
roughly $5 of AI usage per average task
and:
just under 23 hours from start to goal for successful projects in the largest cluster.
The exact economics remain estimates.
But the direction is clear.
AI is making cyberattacks:
cheaper, more scalable and more persistent.
That does not mean every website is suddenly hackable.
It means attackers can afford to investigate many more websites than before.
For website owners, the response is not panic.
It is better security discipline:
Know every site you own.
Patch quickly.
Remove abandoned infrastructure.
Use MFA.
Monitor activity.
Maintain backups.
Secure vendors.
Limit AI-agent permissions.
The era of AI-assisted cybersecurity is already here.
And the same autonomous technology businesses are using to automate legitimate work is increasingly available to criminals as well.